





Summary
A comprehensive guide to configuring the Login tab in Portal Settings, including login methods, access controls, and setting up SSO connections as Service Provider or Identity Provider.
Introduction
The Login tab is where you control how users access your learning portal. Single Sign-On (SSO) allows users to authenticate using one set of credentials across multiple applications, eliminating the need to remember separate passwords. When configured properly, students can access their courses using existing credentials from your organization's identity provider, saving time and improving security while reducing password fatigue. For a complete overview of all Portal Settings tabs, refer to Understanding and Navigating Your Portal Settings in KnowledgeCity LMS.
Requirements
KnowledgeCity LMS administrator with Full Access, or a custom role that grants the Portal Settings section: Required to access and modify Portal Settings.
SSO prerequisites: If setting up SSO, obtain metadata from your identity provider (IdP) before starting.
Subscription availability: Ensure active subscriptions are available for license assignment to new SSO users.
Steps to Follow
Accessing Portal Login Settings
Follow the steps below to access the Login tab:
Sign in to your KnowledgeCity LMS with an administrator account that has Full Access.
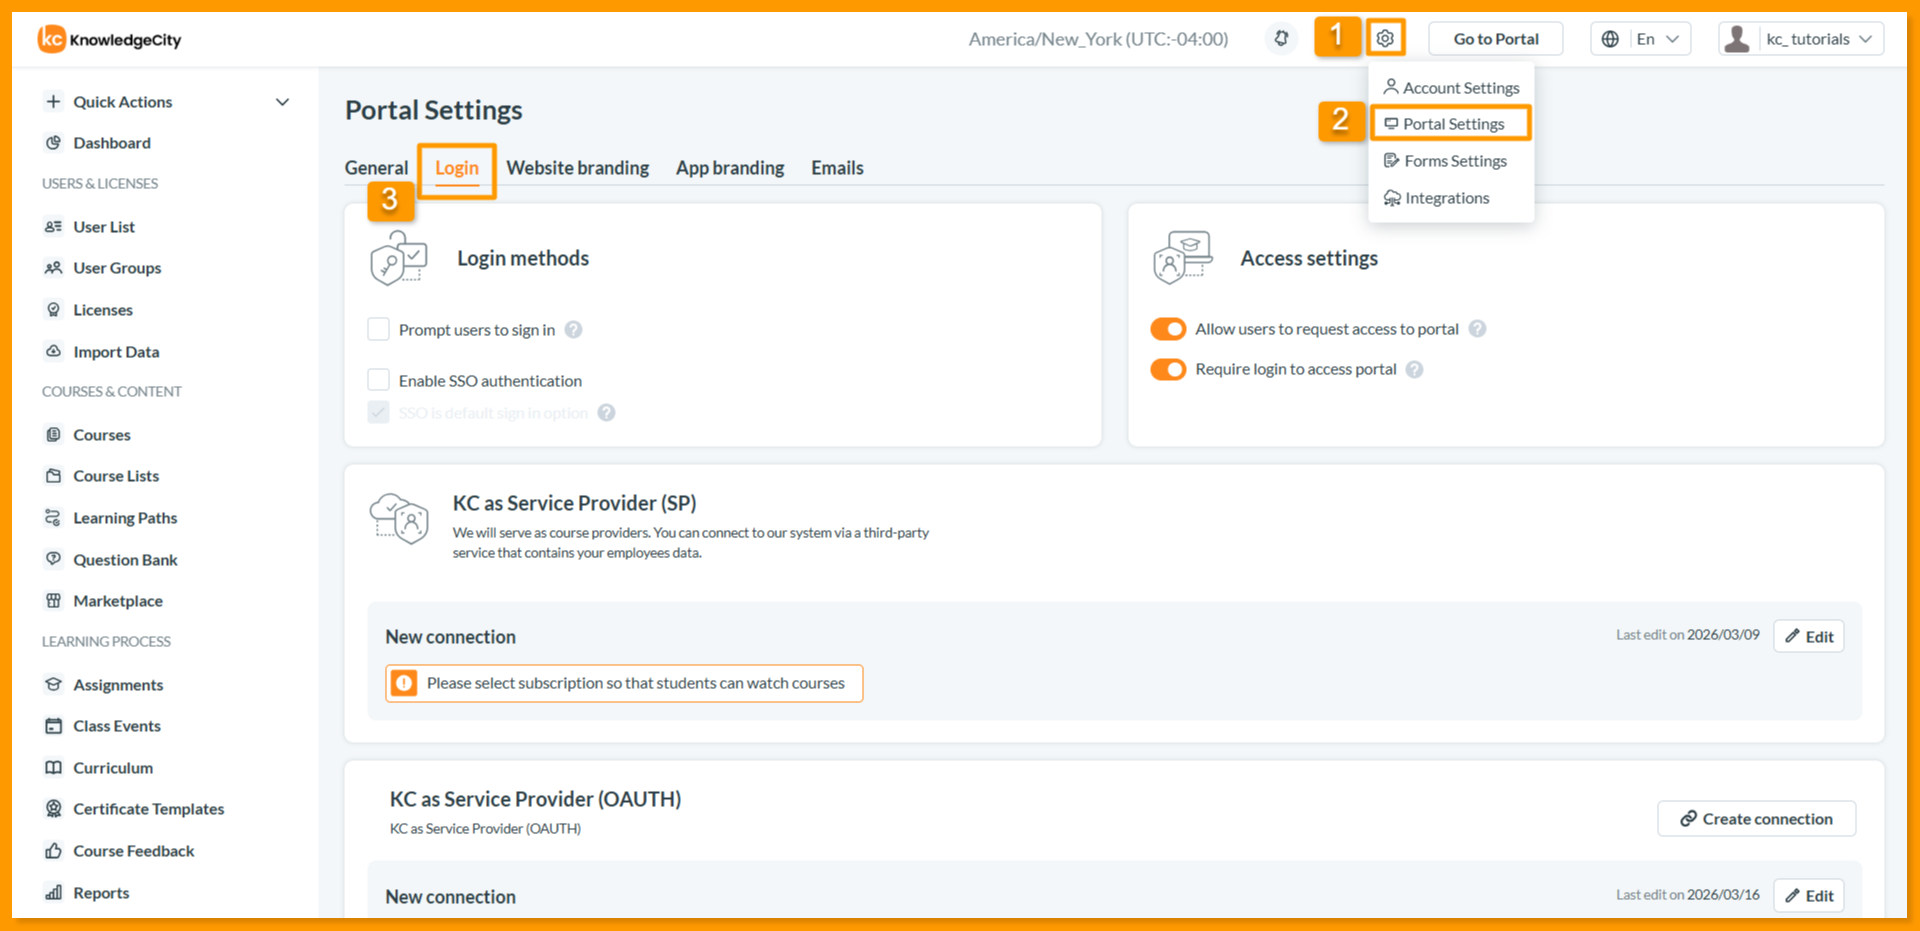
Locate the Settings dropdown menu on the top panel of the LMS interface and select Portal Settings.
Click on the Login tab to access the configuration options.
The Login page is organized into three main sections: Login methods, Access settings, and SSO connections (KC as Service Provider SP, KC as Service Provider OAUTH, and KC as Identity Provider IdP).
Configuring Login Methods
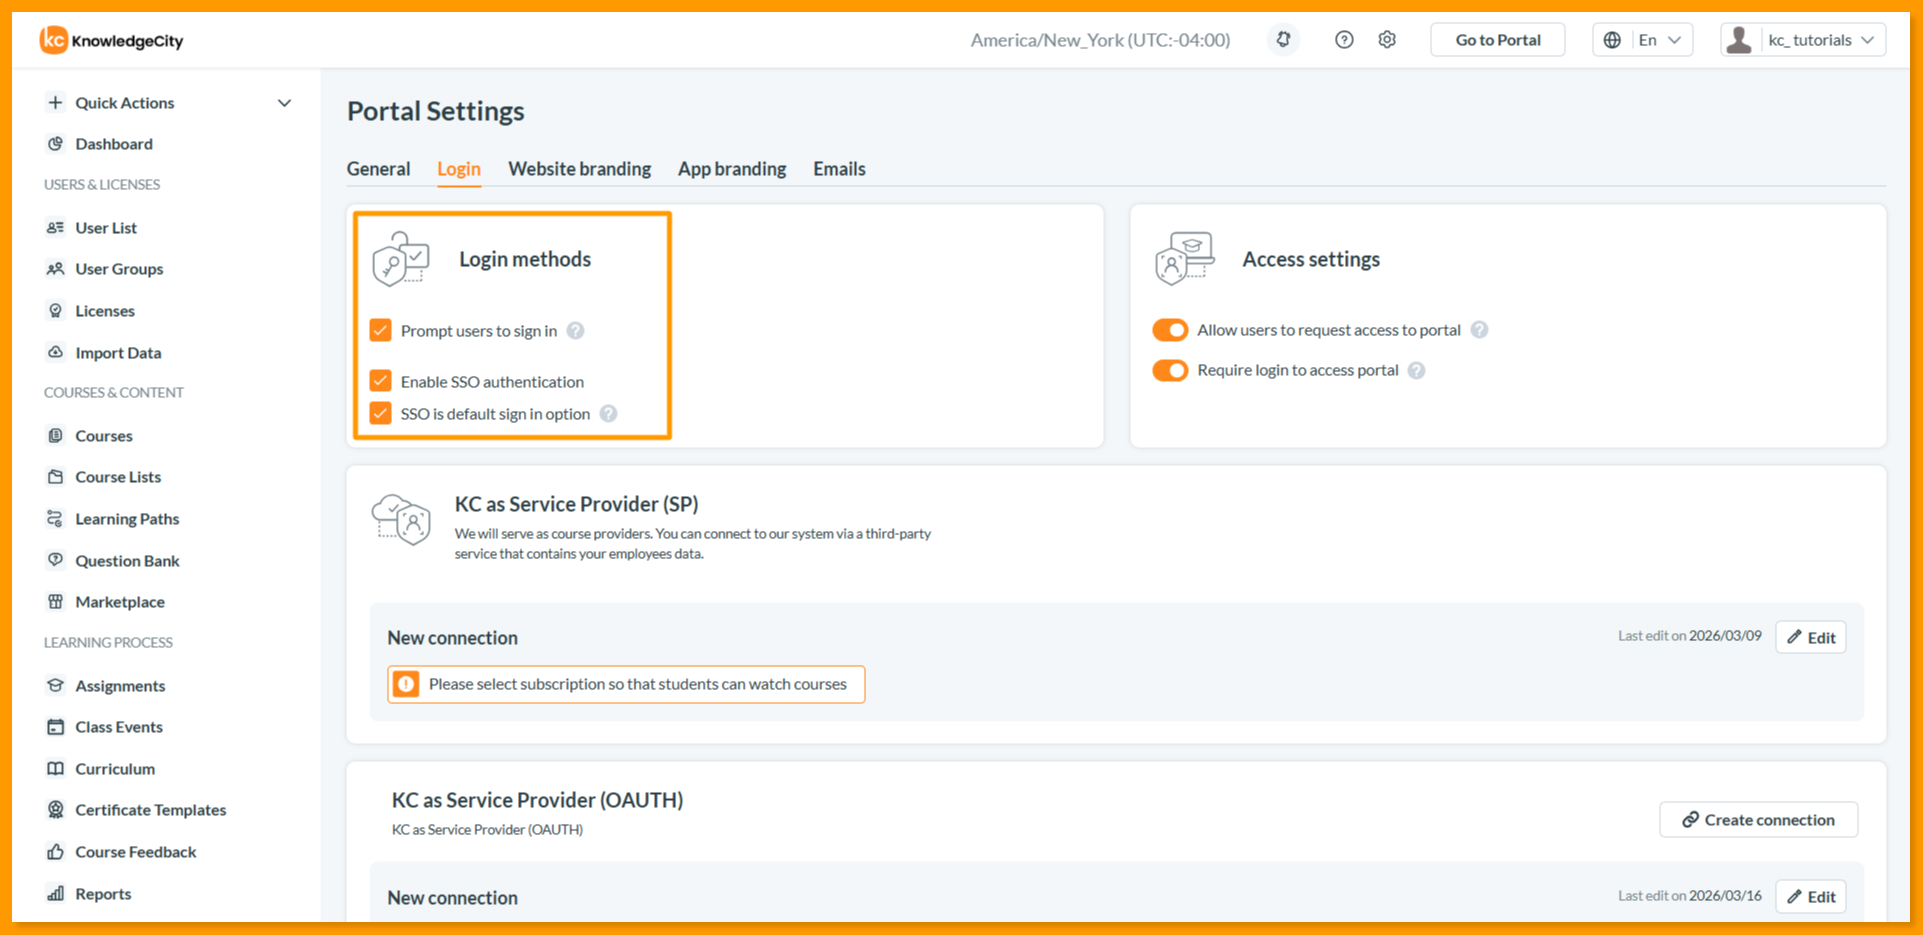
The Login methods section controls how users are prompted to sign in when they visit your learning portal, giving you flexibility over the authentication experience.
Prompt users to sign in: When enabled, a window appears prompting users to sign in upon entering the portal.
Enable SSO authentication: Turns on Single Sign-On functionality, allowing users to authenticate using your company credentials.
SSO is default sign in option: When enabled, users see the SSO sign-in option first before other login methods.
Configuring Access Settings
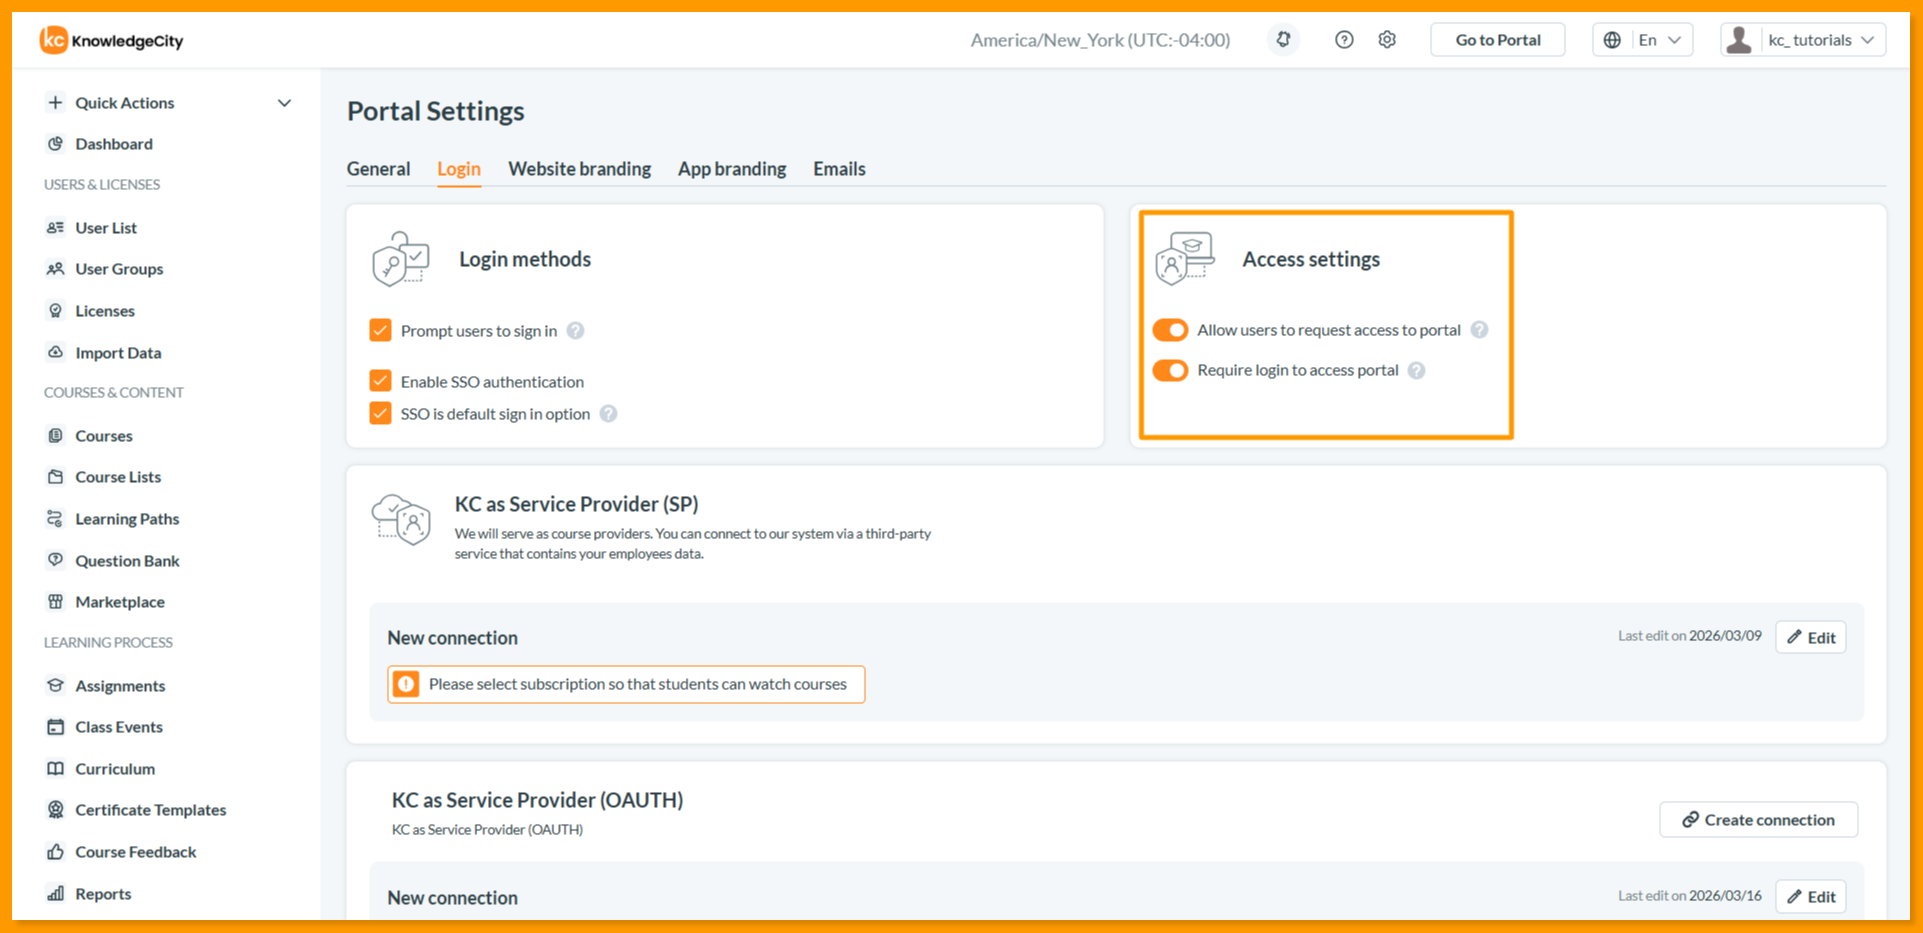
The Access settings section controls who can request access and whether login is required to view learning portal content, helping you maintain security and control.
Allow users to request access to portal: When enabled, users without existing profiles can submit a request for administrators to create a profile and then admins can review to grant portal access. Requests appear in the Access Requests section for approval. For detailed information, refer to How to Manage Access Requests in KnowledgeCity LMS.
Require login to access portal: When enabled, users must sign in before viewing any portal content. This ensures your portal remains private and accessible only to authenticated users.
Configuring SSO Connections
KnowledgeCity LMS supports three types of SSO connections. Each serves a different integration scenario.
KC as Service Provider (SP)
This configuration allows KnowledgeCity to serve as the course provider, connecting to a third-party service that contains your employee data. Your identity provider handles authentication while KC delivers the learning content.
Creating a New SP Connection:
Click the New connection button in the KC as Service Provider (SP) section.
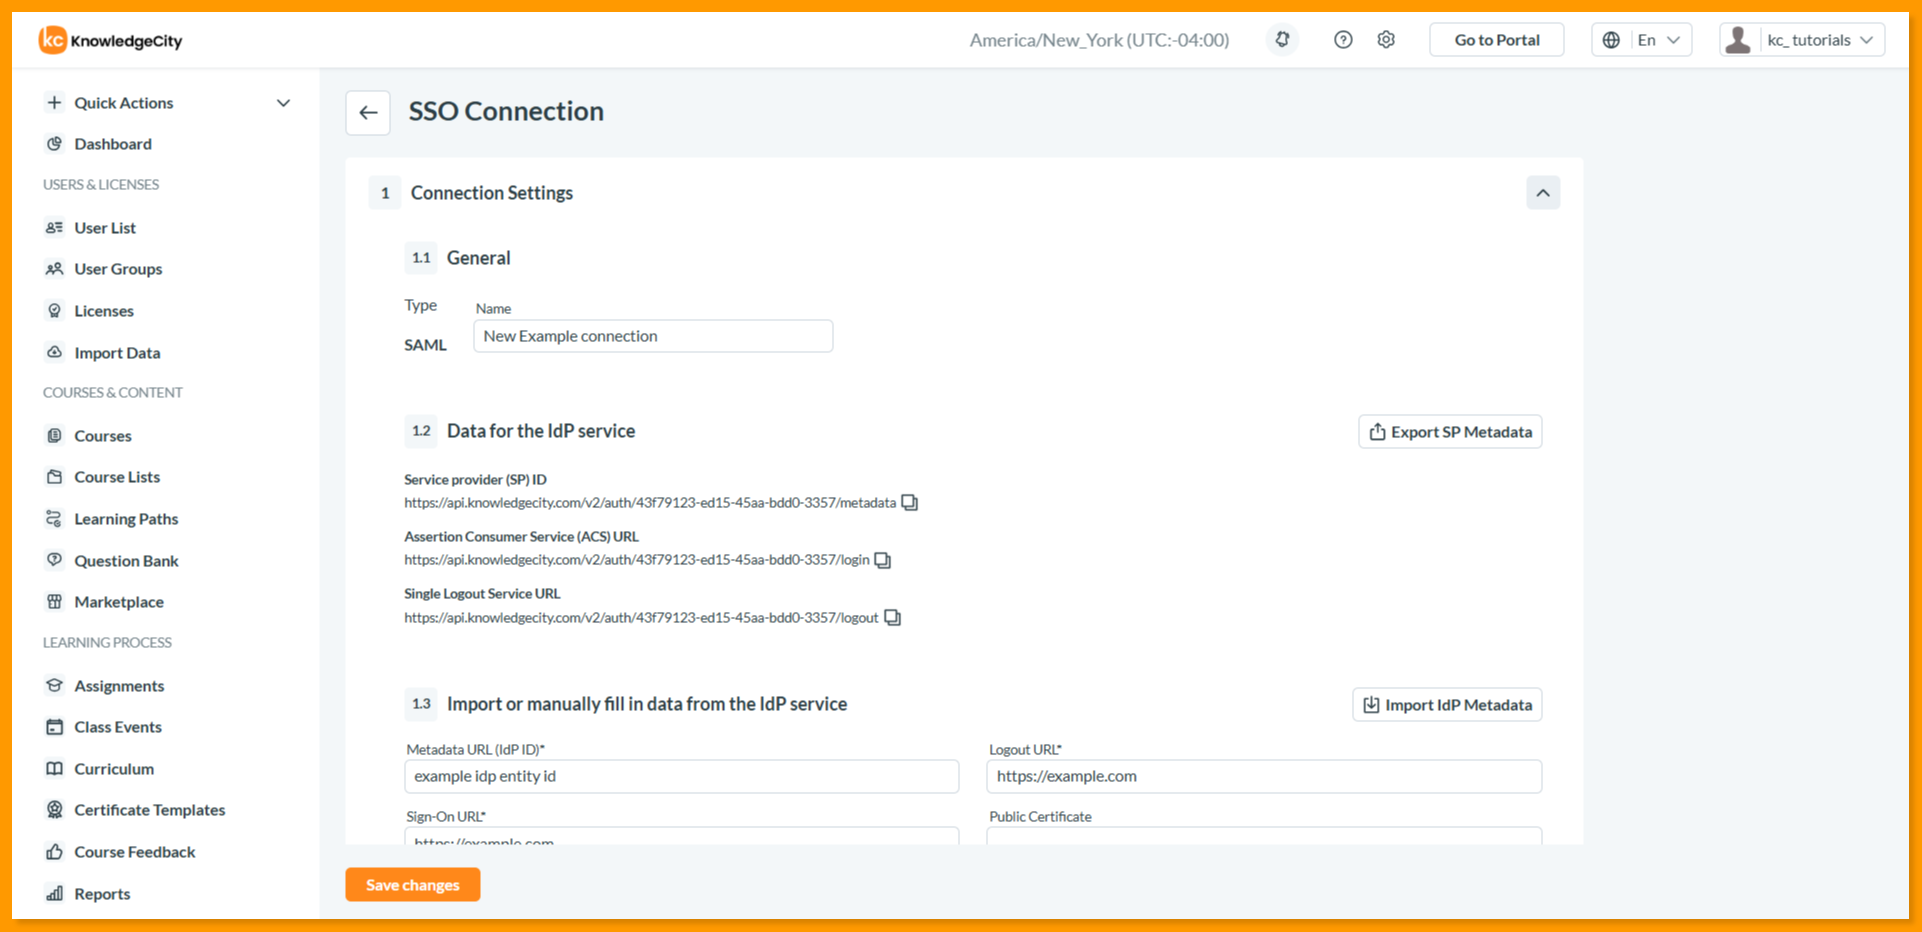
You are redirected to the SSO Connection page with the following configuration panels:
Section | Description |
|---|---|
Connection Settings | Configure general settings, export SP metadata, and import IdP metadata |
Connect to your IdP service | Verify the connection works by redirecting to your IdP and perform test connection |
Subscription Settings | Select a subscription for license assignment to new users |
Additional settings | Configure attribute mapping and other options |
Key Steps for SP Connection:
Export SP Metadata: Download the XML metadata file and provide it to your identity provider. If your IdP cannot import metadata, provide them with:
Service provider (SP) ID
Assertion Consumer Service (ACS) URL
Single Logout Service URL
Import IdP Metadata: After your IdP configures their side, import their metadata back into KnowledgeCity.
Test Connection: Click Test connection to verify the setup. You will be redirected to your IdP for login; successful authentication returns you to KC with a connection status alert.
Configure Attributes: In Additional settings, map user attributes between KC and your IdP. Match at minimum all required KC attributes.
Select Subscription: Choose a subscription so students can watch courses after being created.
Additional Settings Options:
Disable the First Login screen: When checked, users bypass the first login screen after SSO authorization.
Auto assign license: When checked, new users automatically receive a license if available on the account.
KC as Service Provider (OAUTH)
This configuration uses OAuth protocol for SSO integration with supported identity providers, offering a modern standards-based authentication method.
Creating a New OAUTH Connection:
Click the Create connection button in the KC as Service Provider (OAUTH) section.
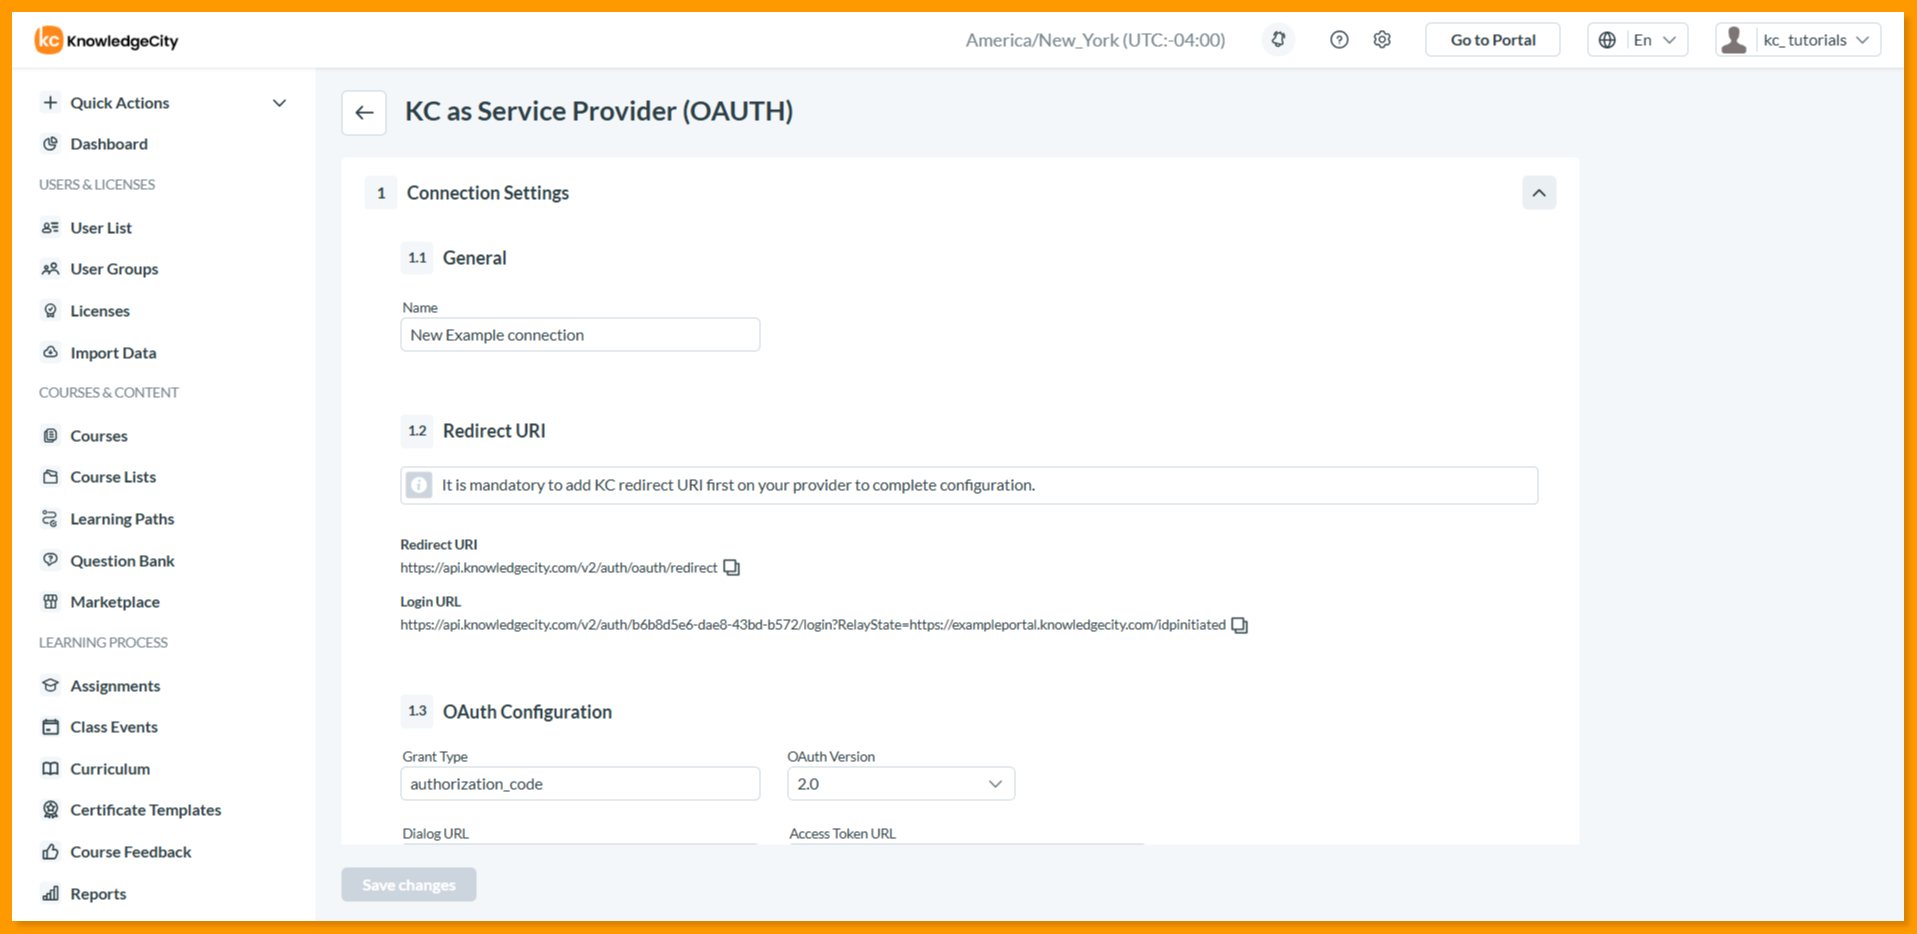
You are redirected to the KC as Service Provider (OAUTH) page with the following configuration:
Redirect URI Whitelisting (Mandatory Step)
When you create a connection, the system generates a Redirect URI. This URI must be added to your Identity Provider's whitelist.
Login URL (User Access URL)
Once the Redirect URI is generated, a Login URL automatically appears. Share this URL with your users, they will access it to authenticate via your IdP and enter KC through SSO.OAuth Configuration Details
Obtain the following information from your Identity Provider:
Field | Description |
|---|---|
Grant Type | Authorization method required by your IdP (e.g., authorization_code) |
OAuth Version | Protocol version (e.g., OAuth 2.0) |
Dialog URL | Authorization endpoint where unauthenticated users are redirected |
Access Token URL | Endpoint for exchanging codes for access tokens |
User Info URL | Endpoint returning authenticated user profile information |
Scope | Permissions requested during authentication (e.g., openid profile email) |
Client ID | Unique identifier registering KC as a trusted application |
Client Secret | Confidential key used by KC to authenticate with your IdP |
Additional panels include Connect to IdP service (test the connection with your provider), Subscription Settings (select or auto-assign licenses for new users), and Additional settings (configure attribute mapping and first login behavior).
Summary Flow: 1. Create connection → 2. Whitelist Redirect URI → 3. Configure OAuth endpoints → 4. Test connection → 5. Share Login URL with users → 6. Users authenticate via IdP and access KnowledgeCity
KC as Identity Provider (IdP)
This configuration allows KnowledgeCity to serve as the identity provider, enabling your students to use KC credentials to authorize on another course platform. KC becomes the source of truth for authentication.
Creating a New IdP Connection:
Click the Create connection button in the KC as Identity Provider (IdP) section.
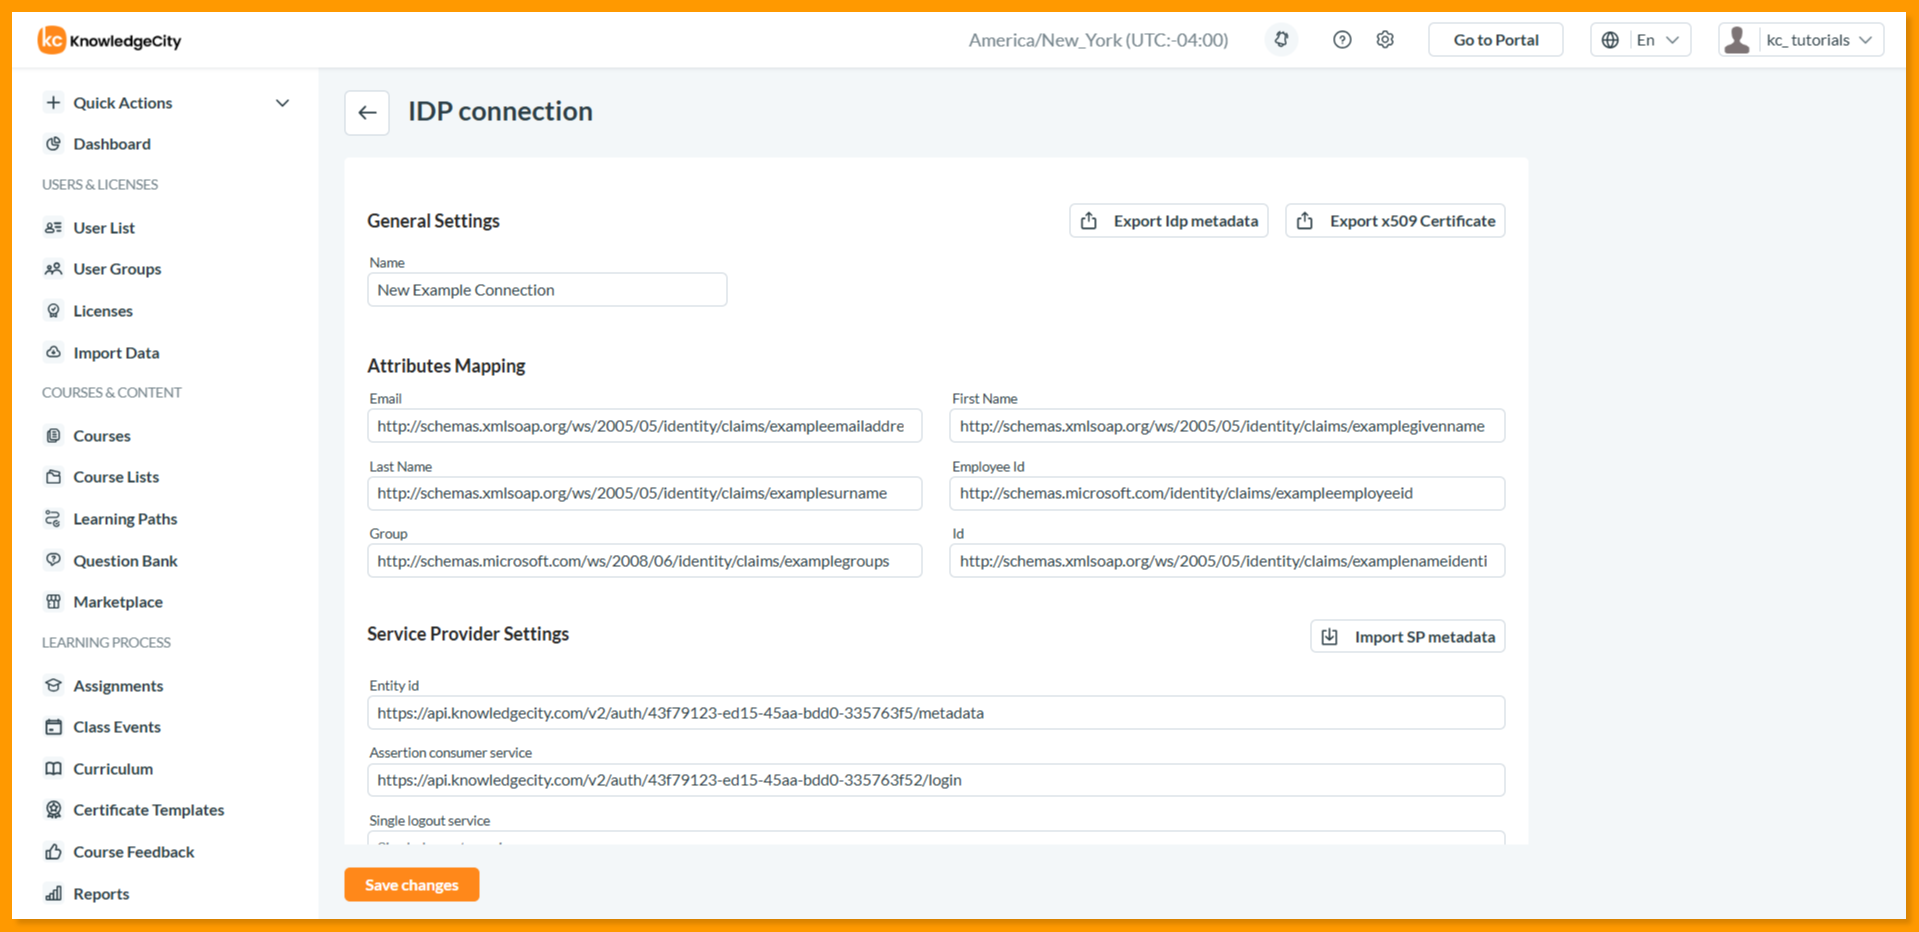
You are redirected to the IDP connection page with the following configuration:
General Settings:
Export Idp metadata: Download metadata to share with service providers.
Export x509 Certificate: Export certificate for secure communication.
Name: Enter a name for the new connection.
Attributes Mapping: Map KC user attributes (Email, First Name, Last Name, Employee Id, Group, Id) to corresponding attributes expected by the service provider.
Service Provider Settings:
Import SP metadata: Upload metadata from the service provider.
Configure Entity id, Assertion consumer service, Single logout service, and x509 certificate.
Public certificate lifetime in days: Set certificate validity period (default 3650 days).
Additional Settings:
SAML subject name id: Specify the attribute to use as subject name.
Attribute hooks: Configure JSON array for attribute hooks.
List of services to check access: Define access control rules.
Multi Auth: Configure multi-authentication options.
Click Save changes to create the connection.
Save Your Changes
After configuring any settings in the Login tab, scroll to the bottom of the page and click Save changes. Changes will not take effect until saved.
Important Notes
SSO default option dependency: The "SSO is default sign in option" setting only takes effect when "Enable SSO authentication" is also turned on. Enabling this option without first activating SSO authentication will have no impact on the login experience.
Access requests: When enabled, admins can manage the Access Requests section for new user requests.
Edit Connection: Each connection section displays the last edit date with an Edit button to modify existing connections.
SSO metadata exchange: Setting up SSO requires exchanging metadata between KnowledgeCity and your identity provider. Export SP metadata and provide it to your IdP, then import their metadata back into KC.
Test connection always: After configuring SSO, always run the connection test to verify everything works before communicating the change to users.
Attribute mapping: Ensure required user attributes are properly mapped between systems, without correct mapping, users may not be able to access content.
License assignment: Select a subscription for new users created via SSO, or enable auto-assign.
Conclusion
You have successfully configured the Login Settings for your KnowledgeCity LMS portal. Login methods, access controls, and SSO connections are now set according to your organization's requirements. These settings ensure secure, seamless access for your learners while maintaining control over who can enter your portal.